I run plex on proxmox. When I woke up I noticed my proxmox server was using a lot more cpu than usual.
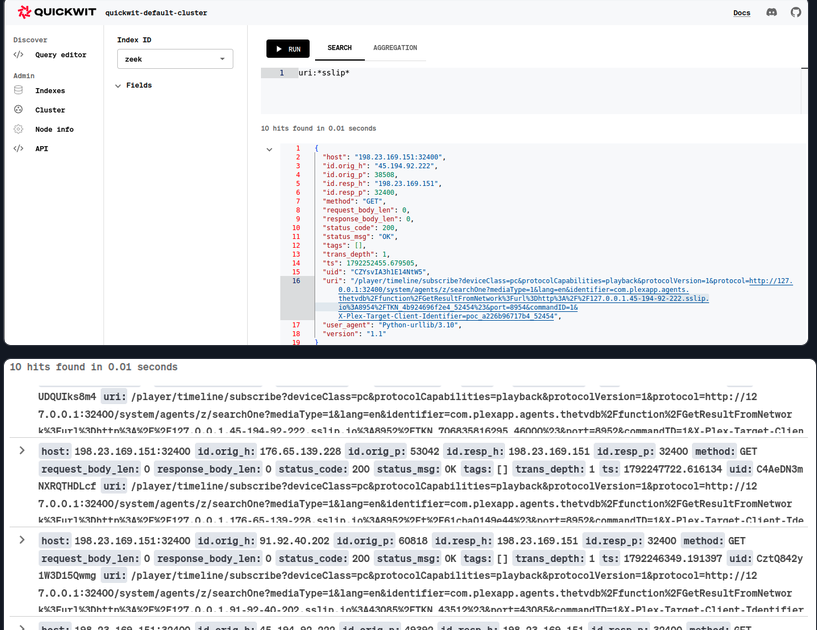
Then, plex was using all the resources it was provisioned for. So I checked out what was running and it was a weird process. I tracked down some logs and found the intrusion. IPs related to it etc. but I just blew up the lxc. Saved a copy of the malicious programs and the logs to dig into. Spun up a new plex from the previous days backup.
They’re cryptographic strings that plex uses to identify you on the back end. You reset them by changing your password and checking the sign out all devices button.


How did you detect and remove it
I run plex on proxmox. When I woke up I noticed my proxmox server was using a lot more cpu than usual.
Then, plex was using all the resources it was provisioned for. So I checked out what was running and it was a weird process. I tracked down some logs and found the intrusion. IPs related to it etc. but I just blew up the lxc. Saved a copy of the malicious programs and the logs to dig into. Spun up a new plex from the previous days backup.
Did you reset your Plex admin keys?
Yeah, in the logs I saw they seemed to get my keys so I reset everything
What are admin keys that you’re referring to?
They’re cryptographic strings that plex uses to identify you on the back end. You reset them by changing your password and checking the sign out all devices button.